heeay
V2EX  ›  WireGuard

请教一个 wireguard 网络出口问题

  •  
  •   heeay · Dec 8, 2021 · 2734 views
    This topic created in 1791 days ago, the information mentioned may be changed or developed.

    图片注释

    4 replies  •  2021-12-08 18:55:14 +08:00
    madao2015
    madao2015
    Dec 8, 2021
    1
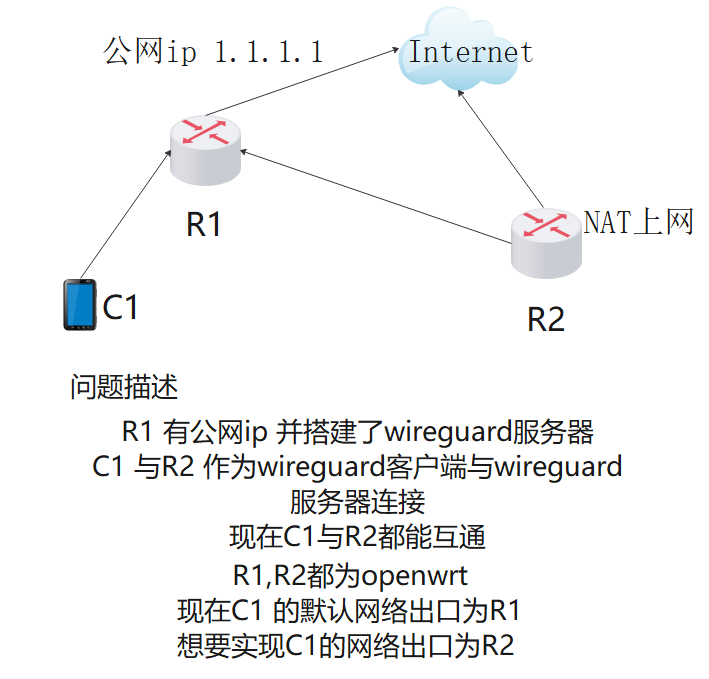
    r1 上应该可以用 iptables 把 c1 的请求转发到 r2 去
    mogita
    mogita
    Dec 8, 2021
    2
    可以试试:在 C1 、R1 的 AllowedIPs 里加上 R2 的内网 IP/32 ,而不填写四个 0 。同时 R1 、R2 的 wg0.conf 里确保开启转发:

    PreUp = sysctl -w net.ipv4.ip_forward=1
    PostUp = iptables -A FORWARD -i %i -j ACCEPT; iptables -t nat -A POSTROUTING -o eth0 -j MASQUERADE
    PostDown = iptables -D FORWARD -i %i -j ACCEPT; iptables -t nat -D POSTROUTING -o eth0 -j MASQUERADE
    heeay
    heeay
    OP
    Dec 8, 2021
    3
    @madao2015 感谢提供思路
    heeay
    heeay
    OP
    Dec 8, 2021
    4
    @ck65 由于 C1 是客户端 如果 AllowedIPs 不写四个 0 就只能路由 wireguard 内网 ip 达不到上述的要求
    About   ·   Help   ·   Advertise   ·   Blog   ·   API   ·   FAQ   ·   Privacy   ·   Solana   ·   1306 Online   Highest 6679   ·     Select Language
    创意工作者们的社区
    World is powered by solitude
    VERSION: 3.9.8.5 · 27ms · UTC 20:00 · PVG 04:00 · LAX 12:00 · JFK 15:00
    ♥ Do have faith in what you're doing.
